How should an AI workspace separate company data?
Company data separation must apply wherever a shared AI service reads, stores, retrieves or changes business information. A tenant means one customer organization, and its boundary should cover files, search, caches, logs and background jobs. Request evidence of access controls and restricted-user tests rather than relying on folder names or model instructions.
Keep these in mind
- Tenant identity should come from trusted authentication.
- Search and cached answers need the same access rules as records.
- Test boundaries with deliberate cross-company examples.
Follow the boundary through the entire request
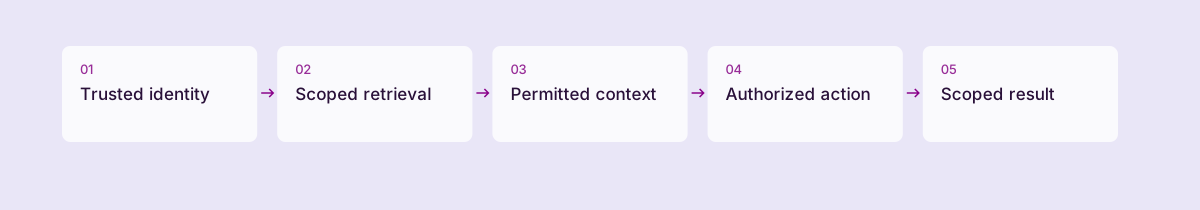
A user signs in to Company A, asks about an order and receives an answer. The trusted session should determine the company.
The record lookup, document search and generated answer should all use that same scope. The user should not be able to change a company identifier in the question to gain another company’s records.
Background work needs the same care. A queued document-processing job can outlive the browser session.
It still needs the correct tenant identity when it reads the file and saves the result. A safe foreground query does not prove a safe background job.
A memory boundary checklist
Use these questions when reviewing an AI workspace with a technical provider. Ask for a demonstration of each boundary using fictional companies and restricted user accounts.
| Component | Failure to test | Useful evidence |
|---|---|---|
| Record lookup | Guess another company’s record ID | Forbidden result without leaked details |
| Search index | Retrieve a similar private document | Permission-filtered results before prompt use |
| Cache | Reuse another tenant’s answer | Tenant and user scope in cache rules |
| File link | Open another company’s attachment | Authorized download checks |
| Background job | Lose company context in a queue | Scoped job identity and write validation |
Database rules can add a layer of protection
PostgreSQL’s row-security documentation explains policies that restrict which rows a user can read or change. It also documents privileged-role exceptions. A technical reviewer should inspect the actual application role and configuration, rather than assume the feature name alone establishes isolation.
Search engines and object storage may use different controls. If a system copies documents into a search index, it must carry the permission information along. A deleted or restricted document should not remain available through an older cached answer or an unrestricted preview.
Run a deliberately confusing trial
Use two fictional businesses with the same contact name and order number. Give each a distinct private phrase in an attachment.
Sign in with a restricted account and ask questions designed to retrieve the other company’s phrase. Try record links, search, exports and error messages.
A failed test should produce a clear, bounded response. It should not reveal that the other company exists or summarize its private record while refusing the final download. Review the full answer and logs, not merely whether the main database screen blocked access.
Retention is part of memory design
An organization may need to correct or delete information. Ask how that change reaches source files, structured records, search indexes, caches and backups.
Retention may differ across these places, and the vendor should explain the boundaries. “The model remembers” is too vague to operate.
Ask the provider to explain the actual arrangement in language the business can use. Record the stores involved, who can authorize access and how changes reach search or cached results.
Choose a small set of acceptance tests and repeat them after significant configuration changes. The useful outcome is evidence that the promised boundaries hold for the workflow you intend to operate.
- Ask how tenant identity is established and carried.
- List every store and retrieval path.
- Test duplicate names and cross-company identifiers.
- Review privileged support and administrator access.
- Verify correction, export and deletion behavior.
Common questions
How can we test company separation in a shared AI workspace?
Create two fictional companies with similar names and order numbers but different private test phrases. Use restricted accounts to try record links, searches, downloads and exports. Verify that unauthorized material is excluded before it reaches an answer or preview.
What should happen to search results when a document becomes restricted?
The restriction needs to reach every relevant retrieval path, including search indexes, cached answers and downloads. Ask the provider how updates propagate and test the result. A changed permission in the main screen is not enough if another route still exposes the content.
Sources & further reading
Primary references for the facts and frameworks discussed. Worked examples and recommendations are Daltn’s own analysis.
- AWS SaaS Lens: Tenant Isolation ↗
Explains tenant separation as an architectural requirement.
- PostgreSQL Row Security Policies ↗
Documents row policies and important privileged-role exceptions.
- AWS SaaS Tenant Isolation Strategies ↗
Provides primary architecture discussion of isolation approaches.
Published by the team building Daltn. Comparisons are first-party analysis, not independent reviews. Our editorial approach.