What should manufacturers check about AI data sovereignty?
AI data sovereignty concerns which locations, organizations and rules govern your business information throughout its use. A virtual private cloud provides network separation, while processing, backups and support access need their own checks. Map sensitive information, inspect the complete service arrangement and confirm requirements with the people responsible for contracts and compliance.
Keep these in mind
- A private network and a data-residency commitment are different things.
- Include model requests, logs, backups and support in the review.
- Use a written evidence checklist before sharing sensitive designs.
Start with the information you need to protect
A bill of materials reveals components and quantities. A drawing may reveal an unreleased design.
A supplier agreement can expose prices and terms. These documents create different risks, so begin by grouping them according to the harm from an unwanted disclosure or change.
For an illustrative machine-parts business, routine delivery dates may be acceptable in the normal workspace. A restricted prototype drawing may require a different process. Avoid granting broad access to a complete folder merely because one file is needed to answer a question.
Understand what a VPC actually supplies
A virtual private cloud is a logically isolated cloud network. AWS’s VPC documentation explains its networking role.
It provides useful infrastructure. Check separately whether connected AI services and backups operate inside that network.
Ask what crosses the boundary. A document parser may send content to another service. An error log may contain extracted text.
An administrator may access the environment from a different country. Each path needs an answer; a diagram showing one private box is incomplete.
Ask five concrete questions
Use this procurement checklist to find unanswered questions. Match the level of evidence to the sensitivity of the documents and the consequences of unwanted access or loss.
| Area | Question | Evidence to request |
|---|---|---|
| Processing | Where are files and model requests processed? | Service and region inventory |
| Access | Who can see content, including support? | Role model and support procedure |
| Retention | How long are originals and logs kept? | Retention and deletion process |
| Recovery | Where do backups and replicas live? | Backup locations and restore test |
| Exit | Can we retrieve and remove our information? | Export sample and deletion boundaries |
Network separation needs operational controls
AWS’s VPC security practices cover traffic controls, identity and monitoring. The useful buying lesson is that a network boundary still needs configuration and ongoing operation. A dedicated environment can also be misconfigured or left unpatched.
Define who manages access and what happens when an employee or contractor leaves. Determine whether production support requires a temporary approval.
Ask how access is logged without copying confidential content into broadly visible logs. The operating procedure matters as much as the diagram.
Keep residency, sovereignty and security distinct
Residency concerns where data is stored or processed. Sovereignty concerns the governing jurisdiction and authority. Security concerns protection against unwanted access, change and loss.
They overlap, but evidence for one does not settle the other two. Confirm the interpretation with the people responsible for the business’s contracts and obligations.
NIST’s AI Risk Management Framework provides a voluntary framework for managing AI risk. It is a way to organize questions, not a certification that a particular deployment is compliant. For a supplier review, assign each unanswered question an owner and a decision date.
A sensible pilot before confidential production use
Test with a sanitized drawing or fictional bill of materials. Keep the workflow useful enough to expose actual storage and support paths, but remove secrets.
Ask a colleague to find the original, export the accepted record and complete a deletion request. This reveals whether the promised controls are usable.
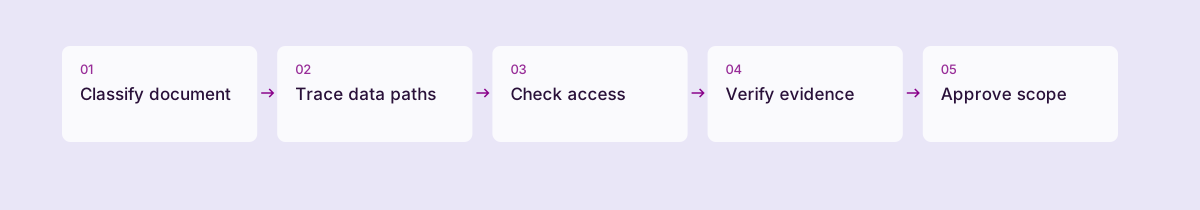
- Classify the documents and define their required boundary.
- Map every processor, storage location and support role.
- Resolve unknowns before sending restricted content.
- Run a sanitized pilot and inspect the evidence.
- Record the approved scope and revisit it after changes.
Make a focused procurement decision
Turn the review into a written decision about one workflow and its permitted information. Record which documents may be shared, which remain restricted and who can approve an exception.
Keep unanswered hosting or access questions open until the provider supplies evidence. Review the decision when a new service, support arrangement or category of sensitive document changes the original assumptions.
Common questions
What evidence should a provider supply about sensitive documents?
Ask for processing and storage locations, service providers, access roles, retention rules and recovery arrangements. Include model requests, logs and backups. Use a sanitized pilot to check that the described controls work for the particular document workflow.
How do residency and security differ?
Residency covers storage and processing locations; security covers protection against unwanted access, change and loss. Evaluate both location and access controls. An agreed location needs appropriate access protection, while strong access controls must still meet location requirements.
Sources & further reading
Primary references for the facts and frameworks discussed. Worked examples and recommendations are Daltn’s own analysis.
- What is Amazon VPC? ↗
Defines the scope of a logically isolated cloud network.
- Security best practices for your VPC ↗
Explains complementary identity, traffic and monitoring controls.
- NIST AI Risk Management Framework ↗
Supports a voluntary, organized risk-management approach.
Published by the team building Daltn. Comparisons are first-party analysis, not independent reviews. Our editorial approach.