What should an AI business audit trail record?
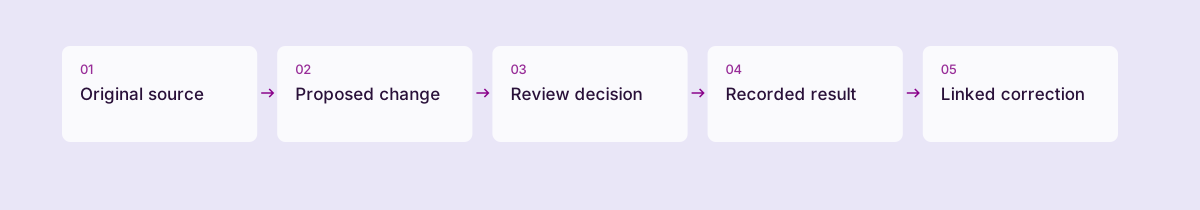
A useful AI audit trail connects the original source, proposed change, reviewer, accepted result and later corrections. It should let an authorized colleague understand what changed and why without reconstructing an entire conversation. Keep evidence accessible, make missing sources visible and avoid collecting unnecessary personal information, passwords or secrets in logs.
Keep these in mind
- Keep evidence and the sequence of decisions connected.
- Show failed and rejected attempts as well as accepted changes.
- Log identifiers and useful context without copying every sensitive detail.
A source link answers only part of the question
Suppose a delivery date changes from Thursday to Friday. A link to a long conversation provides context.
Identify the relevant sentence, associated order and person who accepted its interpretation. The operational record should expose those connections.
A source can establish that somebody said a thing. It does not automatically establish that they had authority or that the statement was true.
Keep “customer requested Friday” separate from “business committed to Friday.” That distinction prevents the audit trail from overstating its own evidence.
Follow a complete fictional change
A supplier sends a revised dispatch date for purchase order P-18. The assistant prepares a change, the buyer notices that the message refers to a sample shipment and rejects it.
A later clarification confirms the full-order date. The buyer then approves a different update.
Both attempts are useful history. If only the final value survives, nobody can explain the earlier confusion.
Retain the rejected proposal and accepted clarification in sequence. Present the current commitment clearly, with the supporting history available when needed.
A practical change record
Use a readable summary backed by stable identifiers. The exact fields depend on the system and retention policy.
| Field | Purpose | Illustrative value |
|---|---|---|
| Target | Which record changed? | Purchase order P-18 |
| Before and after | What actually changed? | Nov 5 to Nov 9 |
| Source | What supported the proposal? | Supplier message, relevant excerpt |
| Decision | Who accepted or rejected it? | Buyer review, timestamp |
| Result | Did the requested change happen? | Saved, failed or superseded |
| Correction | What replaced a mistaken interpretation? | Linked clarification and reason |
Logs should help investigate without creating another leak
OWASP’s Logging Cheat Sheet recommends useful event context and warns against recording secrets and unnecessary sensitive information. The business implication is to capture the action and its identifiers without dumping entire customer records into every log entry.
Keep evidence access restricted. A link in a task should not let an unauthorized user open a private document.
If a retention policy requires source deletion, show that its underlying evidence is unavailable. Keep that limit visible beside the record.
Include the result, not just the request
A log reading “update requested” is incomplete when the database rejected the change. Show whether the action succeeded, failed, timed out or needs review.
A retry should not create a second identical event. A human should be able to distinguish “not done” from “we do not yet know.”
AWS’s transactional-outbox guidance explains the consistency problem when saving a record and sending an event are separate writes. This is an engineering concern behind a simple business expectation: the visible activity history should agree with the accepted record.
Run a reconstruction exercise
Give an authorized colleague an order that changed twice. Ask them to explain the current date, the source and the decision without contacting the original handler. If they cannot, improve the record view before adding more automation.
Agree what evidence the business needs before selecting a logging or record system. A useful operational history shows why a decision was made and what happened afterward. Specialist and statutory processes may need additional controls.
Keep original evidence accessible to the appropriate people. Mark missing or deleted sources so colleagues understand the record’s limits.
- Pick a consequential field such as delivery date or expected amount.
- Inspect its source, proposed values and review decision.
- Check that failed actions are visibly different from completed ones.
- Trace one correction through to the current record.
- Verify that source access follows the user’s permissions.
Common questions
What should an operational change history show?
It should identify the affected record, previous and accepted values, supporting source, decision owner and actual result. Include failed attempts and later corrections where needed. Another authorized person should be able to reconstruct the current state without a verbal recap.
Should an audit log copy every message and attachment?
Record what is necessary for investigation while keeping sensitive evidence under appropriate access controls. Avoid copying passwords, tokens or unrelated personal details into logs. Stable identifiers and linked sources can be more useful than several uncontrolled copies of the same content.
Sources & further reading
Primary references for the facts and frameworks discussed. Worked examples and recommendations are Daltn’s own analysis.
- OWASP Logging Cheat Sheet ↗
Supports useful event context and exclusion of secrets from logs.
- Transactional outbox pattern ↗
Explains consistency risks between saved state and emitted events.
Published by the team building Daltn. Comparisons are first-party analysis, not independent reviews. Our editorial approach.