Could the team continue if the owner’s phone stopped working?
A business continuity plan lets colleagues find active commitments, reach essential records and understand responsibility without the owner’s phone. Check their authorized access, recovery arrangements and ability to answer ordinary operational questions from the available information. Rehearse the handoff safely, then repair the missing access or instruction most likely to stop live work.
Keep these in mind
- Test knowledge access, account recovery and decision ownership as separate concerns.
- Use ordinary authorized accounts instead of sharing the owner’s credentials.
- Test authorized access and recovery with the people covering the work.
Separate the three dependencies
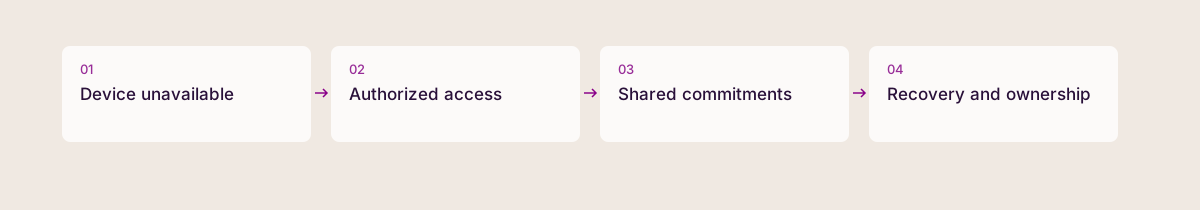
Losing the owner’s phone may remove access to conversations and login codes. Important agreements may also depend on the owner’s memory.
Those are different problems. A backup might address some data loss while doing little to explain which customer instruction is current.
The NIST small-business quick-start guide provides a general framework for cybersecurity and recovery planning. Check where information lives and who can access it.
Then ask how work continues when the device is unavailable. A small rehearsal can expose a missing access arrangement before an actual disruption.
Run the exercise without disrupting live work
Choose a period when the owner can observe and intervene if necessary. Do not disable accounts or remove access merely to make the exercise realistic. Ask a colleague to answer a few ordinary operational questions using their own approved access.
For a service business, start with today’s commitments and outstanding approvals. Check who can confirm requests and find the latest supplier instruction. Record each point where staff need the owner’s device or an unwritten explanation.
| Question | Evidence the team should locate | Gap to record |
|---|---|---|
| What is due today? | Current work and named owners | Commitments known only to the owner |
| What did the customer approve? | Accepted decision and source | Private chat with no shared record |
| Who can decide next? | Decision authority and escalation route | No delegated owner |
| How do we access the tool? | Approved account and recovery method | Single-person access dependency |
| How do we recover data? | Verified backup and restoration process | Untested recovery assumption |
Verify recovery instead of assuming it
The NIST contingency-planning guide discusses recovery planning and testing. Although written for federal information systems, its planning principles can also be adapted voluntarily by other organizations. Review the arrangements for the tools you actually use.
Test account recovery as well as data restoration. The team needs to resume the work, not merely retrieve a folder.
Name the person responsible for account recovery and the person who checks backups or exports where supported. Keep sensitive recovery information in an appropriate controlled place. The handover should tell authorized staff how to get help without exposing credentials in a shared operational note.
Make important business context independent of the device
Move important instructions out of a single person’s memory or private device. The team needs accepted customer commitments, current work and clear responsibility. Check that colleagues can find these through normal authorized access.
Start with a few active jobs and ask a colleague to explain the next step. Their questions reveal what still depends on the owner being present.
Check recovery arrangements for the tools you actually use. Confirm which information is backed up, how authorized staff regain access and who can carry out a restoration.
Keep recovery instructions available through an appropriate separate route. Then test the operational handoff, because recovering files alone does not establish that the team can resume the work.
Repair the most consequential gap first
An exercise can uncover a long list of improvements. Start with the dependency most likely to stop a live commitment.
Check missing access, unknown decision owners and customer instructions nobody else can find. Give it a person and completion date, then repeat that part of the test.
- Select a few active commitments and a safe time for the exercise.
- Ask a colleague to retrieve them using their normal authorized access.
- Record information, account-access and decision-authority gaps separately.
- Verify recovery and backup arrangements with the responsible administrator.
- Move the necessary operational context into a reviewed shared record.
- Retest the repaired dependency and keep the handover current as the team changes.
Common questions
How can a team prepare for the owner losing a phone?
Make active commitments, responsibilities and essential records available through normal authorized accounts. Rehearse a few ordinary questions without using the owner’s device, then repair the missing information or access arrangements.
Is having a backup the same as being ready to continue work?
No. Check how data is restored, how staff regain authorized access and how they identify the next operational step. Test the whole handoff, because recovering files alone does not establish that work can resume.
Sources & further reading
Primary references for the facts and frameworks discussed. Worked examples and recommendations are Daltn’s own analysis.
- NIST Cybersecurity Framework 2.0: Small Business Quick-Start Guide ↗
Small-business cybersecurity risk and recovery planning.
- NIST SP 800-34 Rev. 1: Contingency Planning Guide for Federal Information Systems ↗
Supports contingency planning and recovery testing; federal context is explicitly retained and the operational exercise is an adaptation.
Published by the team building Daltn. Comparisons are first-party analysis, not independent reviews. Our editorial approach.